Cyber Risk Assessment Software Built for Small Businesses & Teams
Uncover your cyber risk in minutes.
Identify cybersecurity gaps.
Prioritize security improvements.
Take action to reduce your risk.
RiskSnap guides you through a simple, self-directed cybersecurity risk assessment and delivers a tailored, actionable report in minutes.
Identify potential security gaps, prioritize improvements, and approach cyber insurance and compliance conversations with greater confidence.
Preparing for launch in 2027.
Great cyber risk management makes small businesses MIGHTY
Because MIGHTY isn't about size. It's about making informed decisions.
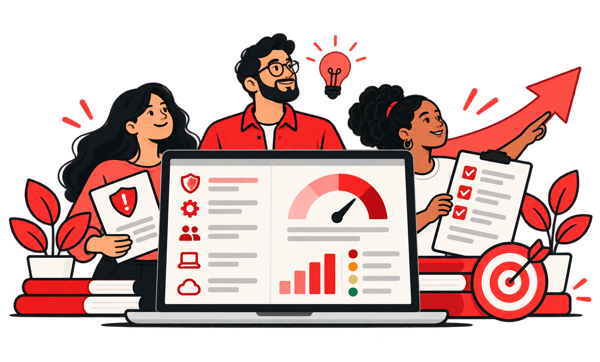
MIGHTY is about understanding the risks your business faces, making smarter decisions, and taking practical steps to protect what matters.
RiskSnap by MIGHTY GRC makes cyber risk management simpler with a guided assessment designed for small businesses. Identify potential security gaps, prioritize improvements, and get an actionable report to help you reduce risk.
No complicated frameworks. No expensive consulting engagements. Just practical insights to help you make better decisions and build a more resilient business.
- Identify cybersecurity risks before they become bigger problems
- Prioritize improvements and make smarter investments
- Prepare for cyber insurance and compliance conversations
- Get more value from your MSP or IT partnership
- Build trust with customers and business partners
- Make informed decisions that support business growth
Six big benefits. One MIGHTY business.
You don't need an enterprise-sized budget or a dedicated cybersecurity department to start managing risk. You need a practical way to understand your vulnerabilities, evaluate your priorities, and take meaningful action.
Understand your risks early and often, before they grow.
Small businesses often operate without a clear picture of their cybersecurity exposure.
RiskSnap helps you identify potential weaknesses in your current practices so you can address important gaps before they contribute to costly disruptions.
Make smarter decisions about technology investments.
Cybersecurity budgets aren't unlimited, especially for small businesses.
With RiskSnap, you can prioritize improvements for more informed conversations about where your time, money, and resources may have the greatest impact.
Prepare for cyber insurance applications and renewals.
Cyber insurance applications ask detailed questions about your risk exposure.
RiskSnap helps you better understand your existing cybersecurity posture and identify areas that may need attention before discussing coverage with your insurer.
Get more strategic IT support from your MSP or technology partner.
Your MSP may understand your technology, but you understand your business priorities.
RiskSnap gives you a clear starting point for discussing cybersecurity concerns, evaluating recommendations, and aligning technology improvements with your business needs.
Build trust with customers, partners, and stakeholders.
Customers and vendors increasingly want reassurance that their data is secure.
Understanding your cybersecurity risks and roadmapping improvements can help you respond confidently to security questionnaires, vendor reviews, and business requirements.
Create a foundation for scalable, confident growth.
New employees, technology, customers, and business opportunities can introduce new risks.
A better understanding of your cybersecurity posture helps you make informed decisions as your business evolves, without allowing unnecessary uncertainty to hold you back.
RiskSnap makes cybersecurity risk assessments more approachable so small businesses can make informed decisions about the people, processes, and technology that protect their operations.
Big business insights without big business complexity.
Understand your risks. Strengthen your policies. Build a more resilient business.
Knowing where your business may be vulnerable is critical. But understanding risk is only useful when you turn those insights into actionable next steps.
RiskSnap by MIGHTY GRC helps you identify potential cybersecurity gaps and prioritize improvements.
PolicyPilot by MIGHTY GRC helps you take the next step by creating, customizing, approving, and maintaining essential business policies that support better security practices and more consistent decision-making.
Together, they make it easier for small businesses to move from identifying risks to putting practical protections in place. No enterprise-level complexity required.
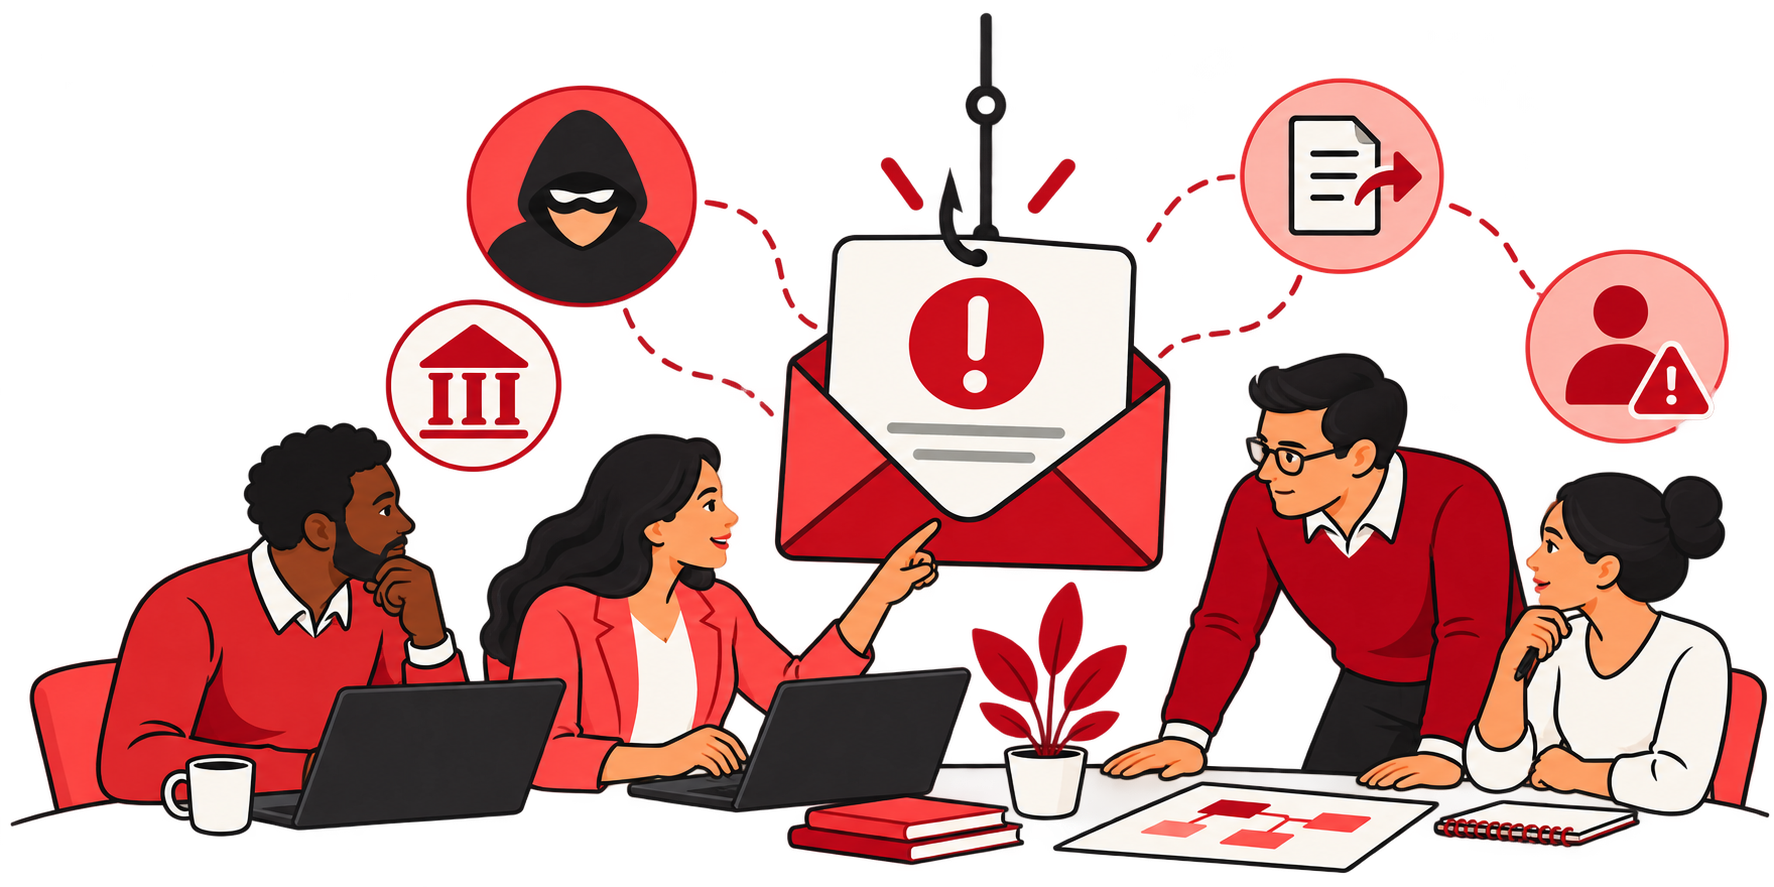
Can Your Team Spot and Stop Email Fraud?
Get your team engaged in building a security-first culture with a free MIGHTY tabletop exercise designed for real-world small businesses and small teams.
Just 60 minutes. No dedicated IT team required.
Frequently Asked Questions
RiskSnap & Risk Assessment Software FAQs
What is cybersecurity risk assessment software?
Cybersecurity risk assessment software helps businesses identify, evaluate, and understand potential security risks affecting their operations, information, and technology.
Rather than relying on assumptions about how secure your business might be, an assessment provides a more structured way to evaluate existing practices, identify potential gaps, and determine where improvements may be needed.
RiskSnap by MIGHTY GRC is being designed to make this process simpler for small businesses. Through straightforward questions and a tailored assessment report, RiskSnap helps you better understand your cybersecurity risks and prioritize practical next steps.
While you wait for RiskSnap to launch, you can explore our flagship product, PolicyPilot. Policy management software purpose built for small business compliance and small business resources.
Does my small business really need a cybersecurity risk assessment?
Yes.
Even small businesses depend on technology, sensitive information, employees, and outside service providers. Each of these can introduce cybersecurity risks.
A cybersecurity risk assessment helps you understand where your business may be vulnerable, evaluate the protections you already have in place, and identify improvements worth considering.
You don't need a large IT department or an enterprise-sized budget to get started. Understanding your risks is an important first step toward building a more resilient business.
Keep exploring: Learn how cybersecurity planning supports long-term business resilience in our MIGHTY Guide to Business Resilience Strategies for Small Business.
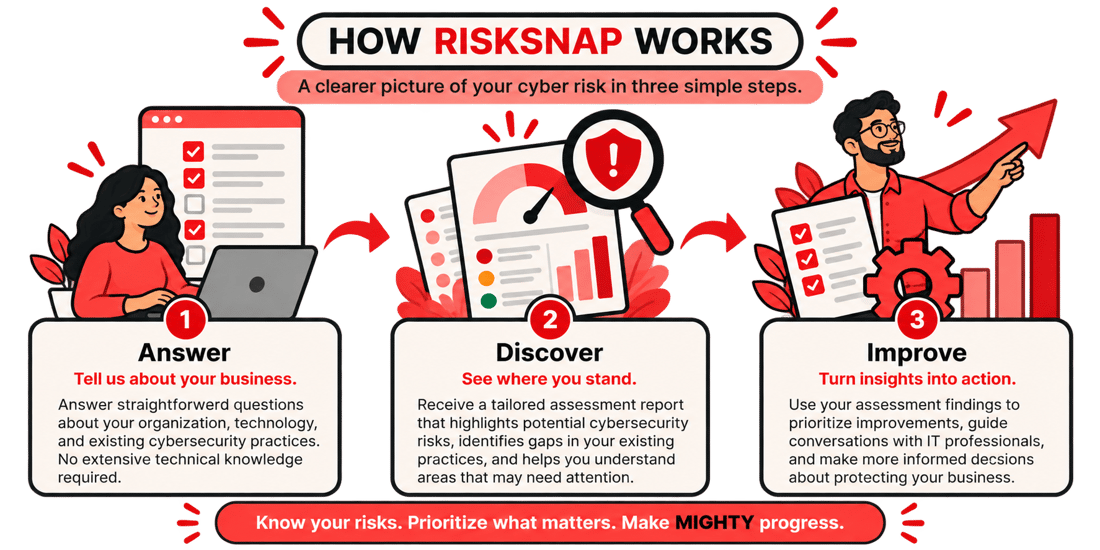
How does RiskSnap work?
RiskSnap is designed around three simple steps:
Answer: Complete a straightforward questionnaire about your business, technology, and existing cybersecurity practices.
Discover: Receive a tailored assessment report highlighting potential cybersecurity risks and gaps in your current practices.
Improve: Use your findings to prioritize improvements, guide conversations with IT professionals, and make more informed decisions about protecting your business.
The goal is to make cybersecurity risk management more accessible, actionable, and genuinely useful for small businesses.
How can I budget for security improvements identified by RiskSnap?
Identifying potential cybersecurity gaps is an important first step, but making improvements often requires planning and financial resources.
RiskSnap helps you understand where your business may be vulnerable and which areas deserve attention.
BudgetLens, coming soon, is being designed to help small businesses anticipate technology expenses and prioritize investments in cybersecurity, infrastructure, and compliance.
Together, they can help you connect cybersecurity priorities with more informed technology budgeting decisions.
Do I need cybersecurity or technical expertise to use RiskSnap?
No.
RiskSnap is being built for business owners, managers, and small teams, including those without dedicated cybersecurity staff.
The assessment is designed to use straightforward questions and practical recommendations rather than overwhelming technical terminology.
However, cybersecurity isn't just about technology. Your employees, everyday practices, and workplace culture all play an important role in protecting your business.
Keep exploring: Learn how to involve your entire team in cybersecurity with our MIGHTY Guide to Building a Security-First Culture.
Can RiskSnap work with my existing MSP or IT provider?
Absolutely.
RiskSnap is intended to complement the expertise of your managed service provider (MSP), internal IT team, or other technology advisors, not replace them.
Your IT partner can help you understand technical risks, evaluate assessment findings, and determine which improvements make sense for your business.
RiskSnap can provide a useful starting point for these conversations by helping you identify potential gaps and clarify your business priorities.
Don't have an MSP? Not every small business needs one, but understanding when outside expertise could help is important.
Keep exploring: Read our guide, Does Your Small Business Need an MSP?, to learn when managed IT services may make sense for your business.
Can RiskSnap help my business with cyber insurance?
RiskSnap is intended to help you better understand your cybersecurity practices and identify potential gaps before cyber insurance applications or renewals.
Cyber insurance questionnaires often ask about security controls, employee practices, incident response procedures, and other measures intended to reduce risk.
Understanding where your business stands can help you prepare for these conversations, identify improvements that may be needed, and work more effectively with your insurance broker or IT advisor.
However, completing a RiskSnap assessment does not guarantee insurance eligibility, coverage, or reduced premiums. Requirements vary by insurer and policy.
Can RiskSnap help with compliance and risk management?
Yes.
RiskSnap is being designed to support small businesses that want a clearer understanding of their cybersecurity risks and existing security practices.
Identifying potential gaps can help you prepare for customer security questionnaires, vendor assessments, cyber insurance discussions, and certain compliance-related requirements.
However, cybersecurity risk assessment software is not a substitute for a formal compliance audit or certification. RiskSnap does not guarantee compliance with any particular law, regulation, or security framework.
For businesses working to establish more consistent security practices, written policies are another important part of managing risk.
Keep exploring: Download The MIGHTY Guide to Seven Essential Policies Every Small Business Should Have to learn which policies can help support your cybersecurity and risk management efforts.
How is RiskSnap different from PolicyPilot?
RiskSnap and PolicyPilot address two complementary parts of business risk management.
RiskSnap helps you understand your risks. It guides you through a cybersecurity assessment to identify potential gaps, evaluate priorities, and determine where improvements may be needed.
PolicyPilot helps you establish and maintain important business policies. It provides tools to create, customize, approve, and review policies that define expectations, responsibilities, and consistent business practices.
Together, they can help your business move from identifying risks to putting better practices in place.
Explore PolicyPilot by MIGHTY GRC to learn how simpler policy management can support your business.
Is RiskSnap a replacement for a professional cybersecurity assessment?
No. RiskSnap is being designed as a self-guided assessment tool that helps small businesses identify potential risks and prioritize improvements based on the information they provide.
It does not independently verify security controls, perform vulnerability scans or penetration testing, or guarantee that every cybersecurity risk will be identified.
For businesses with complex technology environments, specific regulatory obligations, or significant cybersecurity concerns, working with a qualified IT or cybersecurity professional may be appropriate.
RiskSnap is intended to make understanding and managing cybersecurity risk more accessible, not eliminate the value of professional expertise.
How often should my SMB conduct a security risk assessment?
Cybersecurity risk management shouldn't be a one-time activity.
A good starting point for many small businesses is to review their cybersecurity risks at least annually and whenever significant changes occur, such as introducing new technology, expanding operations, changing IT providers, or experiencing a security incident.
The appropriate frequency depends on your business, its risks, and any applicable customer, insurance, or regulatory requirements.
Regular assessments can help you identify emerging concerns, evaluate improvements you've made, and keep your cybersecurity priorities aligned with your business as it grows.
Progress beats perfection. What matters is consistently identifying opportunities to improve and taking meaningful action.
Where can we send your launch notification?