Sometimes even the systems that keep the business up and running.
Those relationships help small businesses do more without having to build every capability in-house. But they also create dependencies. A vendor may have access to your data, connect to your systems, support a critical business function, or simply become something your team can't easily operate without.
That's why you need a vendor risk assessment.
A vendor risk assessment helps you understand the risk a vendor could introduce to your business so that you can decide how comfortable you are with it. And for a small business, it doesn't need to mean sending every vendor a 100-question security questionnaire.
It means asking a few practical questions:
What does this vendor do for us?
What do they have access to?
How much do we depend on them?
What could happen if something went wrong?
Do we know enough to make a good decision?
Here's how to build a vendor risk assessment process that answers those questions without creating more complexity than your business needs.
What is a Vendor Risk Assessment?
A vendor risk assessment is the process of evaluating the potential risks associated with working with a third party.
Depending on the relationship, those risks might include:
Cybersecurity risk
Data privacy risk
Operational risk
Business continuity risk
Financial risk
Legal or regulatory risk
Reputational risk
You may also hear terms like third-party risk assessment, supplier risk assessment, vendor security assessment, or third-party risk management (TPRM).
The terminology can make the process sound more complicated than it needs to be.
At its core, you're just trying to understand what you're trusting another organization with and what that means for your business.
The terminology can make the process sound complicated but you're just trying to understand what you're trusting another organization with.
Even federal guidance recognizes the importance of making this process practical. CISA, the Cybersecurity and Infrastructure Security Agency, has developed vendor assessment guidance specifically for small and midsized businesses, including use cases involving cloud services, vendors with physical or logical access, and managed service providers.
How to conduct a Vendor Risk Assessment in 12 simple steps
You don't need an enterprise vendor management platform to understand your third-party risk.
You do need a repeatable way to identify the vendors that matter the most for your business to operate, understand the risks they introduce, and decide what to do about those risks, if anything.
Here's where to start.
1. Start with the vendors you already use
Before you start thinking about risk levels, questionnaires, or due diligence, start with something simpler:
Who are my vendors?
Create a simple vendor inventory that includes the companies your business relies on for technology, services, operations, and other important functions.
That could include your:
Payroll provider
Accounting software
Cloud storage provider
Email platform
CRM
Payment processor
Managed service provider (MSP)
IT or cybersecurity provider
HR platform
Marketing platforms
Website host
Contractors or consultants
Key suppliers
Don't worry about making the list perfect on day one.
The goal is visibility.
For each vendor, start by recording basic information such as the vendor name, service provided, internal owner, contact information, contract or renewal date, and whether the vendor has access to company systems or information.
You can add more detail as your process matures.
You can't manage what you can't see.
Your vendor list doesn't need to be perfect to be useful.
Start with what you know. Build visibility. Then improve it over time.
A simple list of the businesses your company depends on is already a meaningful step toward understanding your risk.
2. Understand what each vendor does for your team or business
Next, ask:
Why do we use this vendor?
That may sound obvious, but understanding the vendor's role in your business, team, and operations helps you better appreciate and assess the risk associated with the relationship.
Consider:
What service does the vendor provide?
Who uses it?
What business process does it support?
Is the vendor replacing something your team would otherwise need to do?
Would employees be able to work without it?
Would customers notice if it stopped working?
A vendor that provides occasional graphic design services creates a very different dependency than the cloud platform running your customer database.
Understanding the vendor's role comes before assessing the vendor's risk.
Understanding the vendor's role comes before assessing the vendor's risk.
3. Identify what the vendor has access to
Now look at what you're trusting the vendor with.
Also consider whether the vendor stores, processes, transmits, or can access that information.
In other words, don't just ask whether a vendor can see your information. Ask what they can do with it. Can they use it, copy it, modify it, or share it internally or with other third parties without your knowledge or approval?
We want to understand not only access, but ability to act.
Does the vendor have access to:
Customer information?
Employee information?
Financial information?
Confidential business information?
Credentials or user accounts?
Your network?
Cloud systems?
Company devices?
Physical facilities?
The Federal Trade Commission, or FTC, specifically recommends limiting vendor access to sensitive information on a need-to-know basis and only for as long as the vendor needs that access.
The more sensitive the access, the more carefully you'll generally want to evaluate the relationship.
4. Ask what would happen if the vendor was suddenly not available
Vendor risk isn't only about data breaches.
Sometimes the biggest risk to your small business is simply that the vendor would stop working or experience a disruption.
Ask yourself:
What happens to our business if this vendor becomes unavailable tomorrow?
Would you experience:
A minor inconvenience?
A temporary workaround?
Employees unable to work?
Customers unable to access your services?
An inability to process payments?
Lost access to important information?
A major interruption to operations?
Then consider how long you could reasonably operate without the vendor.
An application that saves your team a little time is different from a platform your entire business depends on every day.
This is also where vendor risk management and business continuity start to overlap.
If losing a vendor could interrupt a critical business function, your Business Continuity Plan should account for that dependency.
That means thinking beyond the vendor assessment itself.
How would you keep that part of your business moving if the vendor suddenly became unavailable?
You might need a temporary workaround, an alternate provider, access to important data outside the vendor's system, or simply a clear plan for what your team should do next. Identifying those options before you need them can turn a vendor outage from a scramble into a manageable disruption.
Not sure where to start? Our step-by-step Business Continuity guide walks you through identifying critical business functions, understanding what they depend on, and creating practical Plan B and Plan C options.
5. Determine each vendor's risk level
You now know two important things:
What are we trusting this vendor with?
and
How much do we depend on them?
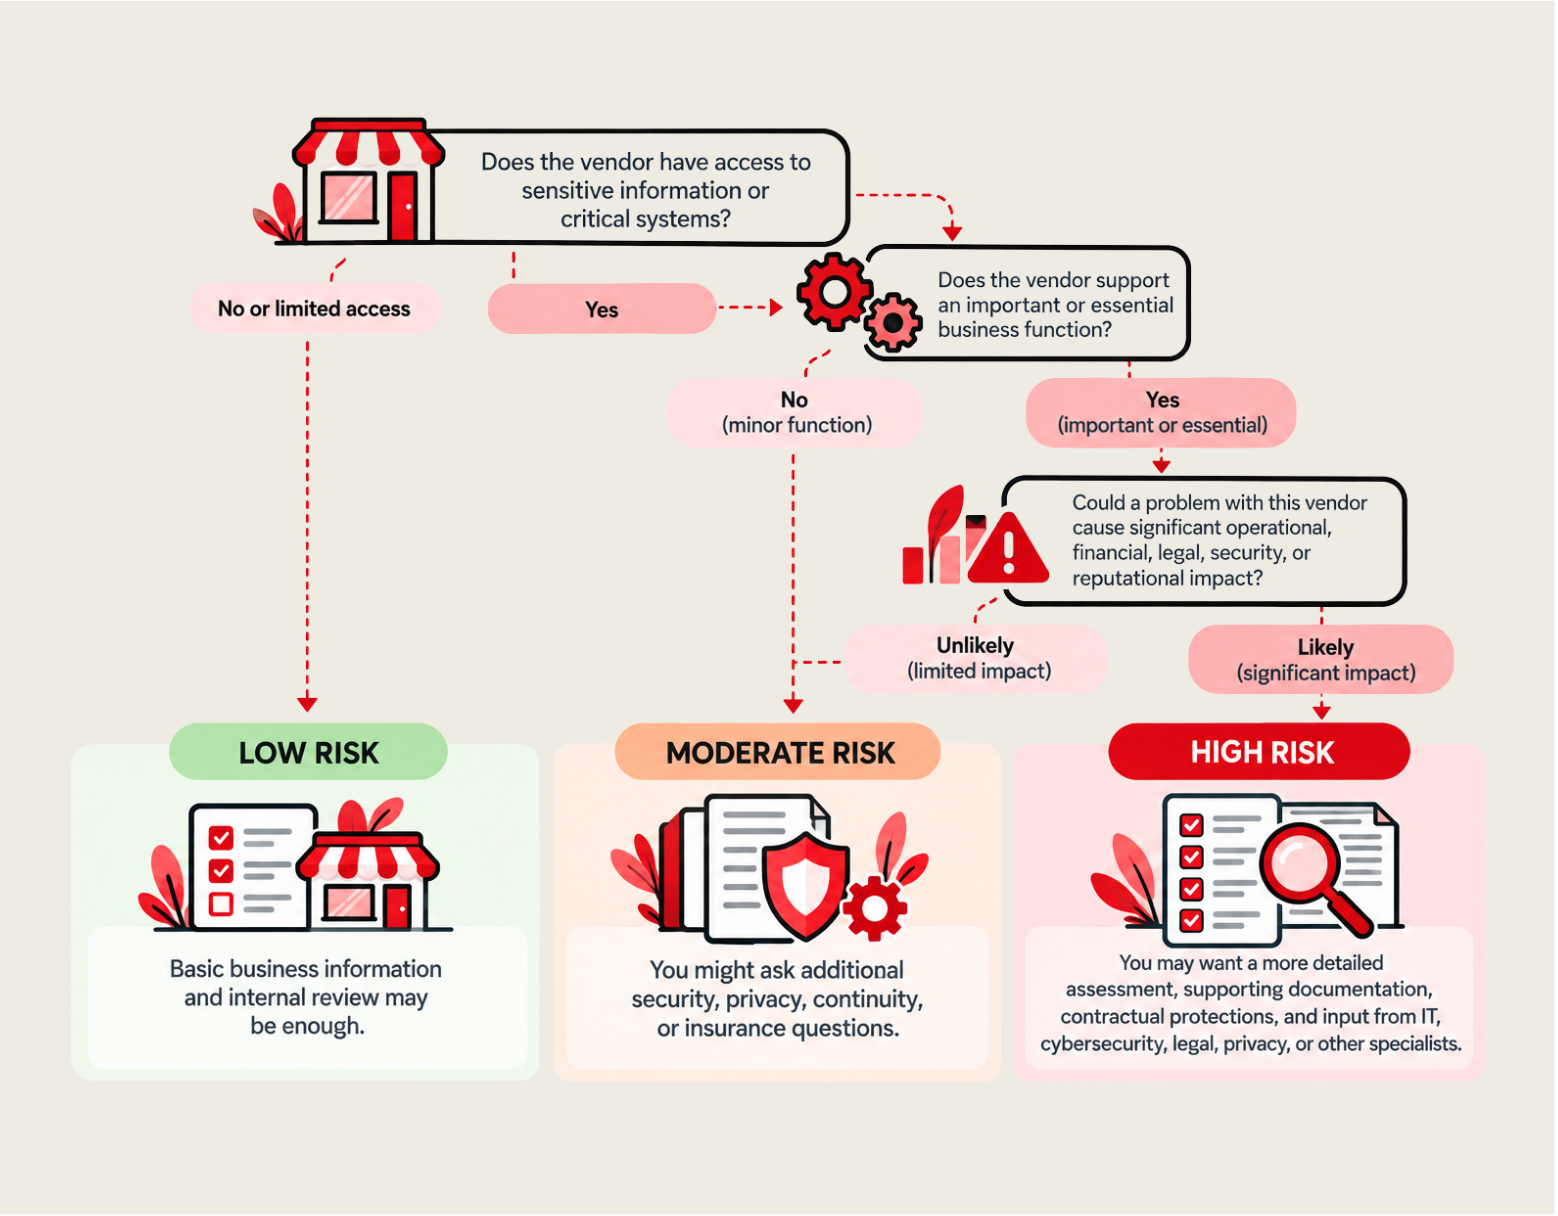
Use that information to assign a simple risk level to each vendor.
For many small businesses, something as straightforward as Low, Moderate, or High may be enough.
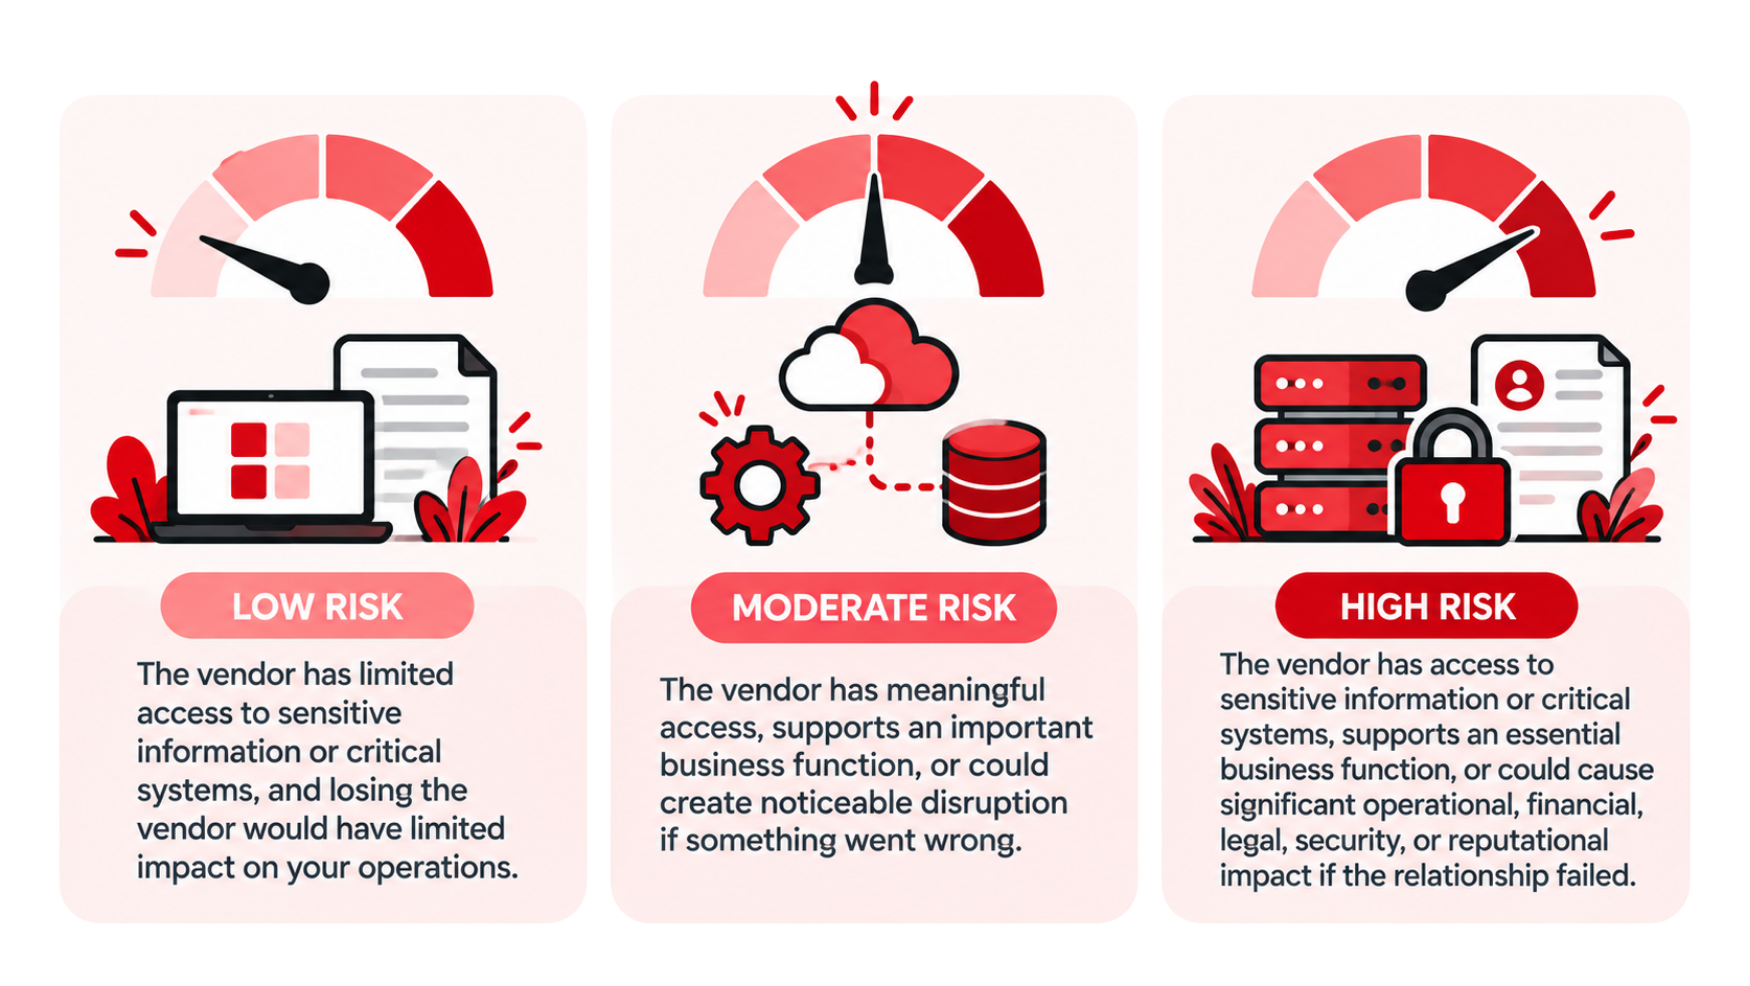
Low risk
The vendor has limited access to sensitive information or critical systems, and losing the vendor would have limited impact on your operations.
Moderate risk
The vendor has meaningful access, supports an important business function, or could create noticeable disruption if something went wrong.
High risk
The vendor has access to sensitive information or critical systems, supports an essential business function, or could cause significant operational, financial, legal, security, or reputational impact if the relationship failed.
Your categories don't have to be sophisticated.
They need to help you answer one important question: How closely should we assess and evaluate this vendor?
6. Match the due diligence to the risk level
This is where vendor risk management can become unnecessarily complicated.
A company providing snacks for your office probably doesn't need the same cybersecurity assessment as the MSP with administrative access to your network.
That doesn't mean the first vendor has zero risk.
The level of effort you put into a vendor assessment should make sense for the level of risk the vendor poses to your small business.
It means that as a small business, your resources are veyr likely limited. The level of effort you put into a vendor assessment should make sense for the level of risk.
Low risk vendor
Basic business information and internal review may be enough.
Moderate risk vendor
You might ask additional security, privacy, continuity, or insurance questions.
High risk vendor
You may want a more detailed assessment, supporting documentation, contractual protections, and input from IT, cybersecurity, legal, privacy, or other specialists.
Save and share this infographic with your team!
This risk-based approach is consistent with current federal guidance. The National Institute of Standards and Technology, or NIST's, 2026 cybersecurity supply-chain due-diligence guide is designed around performing reasonable research on suppliers so organizations can make informed acquisition decisions, including in environments where resources are limited.
Match the effort to the risk
Not every vendor needs a 100-question security assessment.
Spend your time where it matters most.
The more important a vendor is to your operations, the more sensitive the information they can access, or the greater the potential impact if something goes wrong, the more closely you should look.
Good vendor risk management isn't about assessing everything equally. It's about knowing where to look closer to conserve small business resources while ensuring the benefits of your third party risk assessment processes.
Once you know how closely you need to evaluate a vendor, you can decide what you actually need to know.
For technology vendors, for instance, you may want to dig a little deeper.
That could mean looking at their security practices, how they access and use your data, their Business Continuity and Disaster Recovery (BCDR) plans, and other areas that could create risk for your business or impact your day-to-day operations.
Security
Does the vendor have documented information security practices?
Does it use multi-factor authentication?
How does it control access to customer information?
Does it encrypt sensitive data?
How does it identify and address vulnerabilities?
Data
What information will the vendor receive?
Where is that information stored?
Who can access it?
Does the vendor share information with other parties?
What happens to your information when the relationship ends?
Incident response
Does the vendor have an incident response process?
How will it notify you if your information or systems are affected?
Who would you contact during an incident?
Business continuity
Does the vendor have backup and recovery capabilities?
How does it prepare for disruptions?
What happens if its primary systems become unavailable?
People and access
Which vendor employees can access your information or systems?
How is that access approved?
How is access removed when it is no longer needed?
You don't necessarily need to ask every question.
Ask the questions that help you understand the risks that actually matter to yourbusiness.
The vendor questionnaire is not the goal.
The vendor questionnaire is a tool.
Government and industry templates can give you an excellent starting point. That doesn't mean every small business needs to ask every vendor every question.
Start with the risk the vendor creates for your business, then choose the level of due diligence that makes sense.
8. Review the evidence that matters
A questionnaire tells you what a vendor says, or is willing to admit, about its practices, processes, and people.
For higher-risk relationships, you may also want evidence to back up what they state in order to help you evaluate their answers for risk to your business, your team, and your operations.
Depending on the vendor and the risk involved, that could include:
SOC 2 reports
Independent security assessments
Security or privacy certifications
Cyber insurance documentation
Penetration-testing information
Information security policies
Business continuity information
Incident response documentation
Privacy documentation
Audit reports
That doesn't mean collecting every document a vendor can provide.
More paperwork isn't automatically more assurance.
Focus on evidence that helps you answer the questions that really matter to your decision.
The FTC similarly advises businesses to establish processes for verifying that vendors are meeting security requirements rather than relying exclusively on vendor assurances.
9. Understand what's in the contract
Your assessment shouldn't stop when you decide that a vendor appears trustworthy.
The contract turns expectations into commitments.
It helps define what happens after you enter the relationship and can provide important legal and financial protections if something goes wrong.
For higher-risk vendors especially, it's worth making sure the contract reflects the responsibilities, protections, and expectations that matter to your business.
The contract turns expectations into commitments.
Depending on the vendor, consider provisions addressing:
Information security requirements
Data ownership and use
Privacy requirements
Access to systems and information
Breach or incident notification
Business continuity expectations
Service availability
Subcontractors
Cyber insurance
Data retention
Data return or deletion
Termination of the relationship
The FTC recommends putting security expectations into vendor contracts, including requirements related to how data can be used, shared, retained, and deleted, and updating controls as threats change.
For important contracts, this is also a good place to involve legal counsel or seek support from an expert or a dedicated GRC tool.
You don't have to become a contract expert.
You need to recognize when the decision deserves one.
10. Decide what you'll do about the risk
A vendor risk assessment isn't useful or actionable if it ends up simply being a completed questionnaire sitting in a folder.
The purpose is to make an informed decision about each of your vendors and partners.
Does the value of the relationship make sense given the risk it introduces? If so, are you comfortable accepting that risk as-is, or are there reasonable steps you can take to reduce it?
You might decide to:
Approve the vendor as-is
Approve the vendor with conditions
Ask the vendor to address a concern
Reduce the vendor's access
Add contractual protections
Implement additional controls on your side
Create a backup or alternate vendor
Accept a known risk
Choose a different vendor
There isn't always a perfectly safe option.
And that's okay.
Vendor risk management is about making informed decisions, not eliminating every possible risk.
Vendor risk management is about making informed decisions, not eliminating every possible risk.
NIST describes due diligence as researching pertinent information about a supplier or product so organizations can make informed decisions about new acquisitions or existing systems.
That distinction matters.
Risk management isn't about making every risk disappear. It's about understanding enough to decide what makes sense for your business.
11. Document your decision
Once you've made a decision about a vendor and its risk level for your small business, record it. Capture what you decided, what you learned during the assessment, and the factors that ultimately shaped your decision.
This creates a record of why your business made the decision, not just what it decided. That context can save time later when you're evaluating similar vendors, comparing multiple vendors that support the same business function, or revisiting an existing relationship as your business needs or risk tolerance change.
Instead of starting the decision-making process over, you'll have a clear record of what you considered, what you learned, and why the vendor made sense for your business at the time.
At a minimum, you should document:
Vendor
Service provided
Business owner
Information or systems accessed
Business dependency
Risk level
Assessment date
Key findings
Decision
Person who approved the decision
Follow-up actions
Next review date
This documentation may be particularly valuable as your team grows.
Six months later, someone shouldn't have to reconstruct an entire vendor decision from emails, Slack messages, contracts, and someone's memory.
Good governance creates organizational memory.
A good decision becomes more valuable when your business can remember why it made it.
Documenting vendor decisions helps knowledge stay with the business instead of living only in one person's head.
That creates continuity, makes future reviews easier, and helps your team make more consistent decisions over time.
And that's one of the less obvious ways good policies can improve productivity.
When your process, expectations, and past decisions are documented, your team doesn't have to recreate the same knowledge every time a question comes up.
People can find what they need, make decisions with greater confidence, and spend less time tracking down answers or waiting for the person who knows what happened last time.
Approving a vendor isn't a one-time process for your small business.
Vendor risk management is an ongoing effort to understand and respond to the risks your vendors, partners, and other third parties introduce in the normal course of doing business.
Because, in business, things change all the time.
The vendor may:
Launch new products
Change how it handles your information
Gain access to additional systems
Use new subcontractors
Experience a security incident
Change ownership
Change its security practices
Your business changes too.
A piece of software that was relatively unimportant when five employees used it might become critical when your entire company depends on it.
Set a review frequency that makes sense based on risk.
Higher-risk vendors may deserve more frequent review. Lower-risk vendors may only need to be reconsidered periodically or when something significant changes.
The FTC recommends continuing to monitor vendor security and making changes as cybersecurity threats evolve.
Vendor risk management isn't about a lack of trust
Strong vendor relationships are incredibly valuable to small businesses.
They give you access to technology, expertise, infrastructure, and capabilities you might never make sense to build internally.
Vendor risk management isn't about treating your partners like a threat, either. It's about understanding the relationship and working together on the things that matter most.
Better visibility into shared risks, responsibilities, and dependencies can help you and your vendors build more secure, resilient businesses.
What are we trusting this vendor with?
How important are they to our business?
What have we done to understand the risk?
And what would we do if something changed?
Those questions allow you to choose vendors with greater confidence while preparing for the dependencies that naturally come with running a modern business.
Your business doesn't operate alone.
Strong businesses don't eliminate dependencies. They understand them.
The vendors your business relies on expands on what your team can accomplish alone.
Knowing where those relationships create risk helps you make better decisions about where to build safeguards, where to create alternatives, and where you're comfortable accepting the risk.
Understanding your dependencies is part of building a more resilient, scalable business.
Can a Vendor Risk Assessment be DIY?
Absolutely.
In fact, your team should play an important role because you understand your business better than anyone else.
You know which systems matter. You know which vendors employees rely on. You know what information you handle and what would happen if an important service suddenly disappeared.
But there may be parts of an assessment where additional expertise is valuable.
For example:
Your IT provider or MSP can help you understand technical access and system dependencies.
A cybersecurity professional can help evaluate security practices and technical evidence.
Legal counsel can help evaluate contracts, privacy obligations, liability, and notification requirements.
Your insurance professional can help you understand how vendor relationships interact with your coverage.
Policy management software can help you turn your decisions into a repeatable vendor risk process, document how assessments should be conducted, and make sure reviews don't disappear from the calendar.
Scalable small business rule no. 1: Expertise doesn't have to live in-house
Small businesses don't need specialists for every situation sitting on their internal teams. The goal is to understand where additional expertise matters and know who to involve when it does.
You don't have to know everything to be resilient. You need to know where to turn, and when.
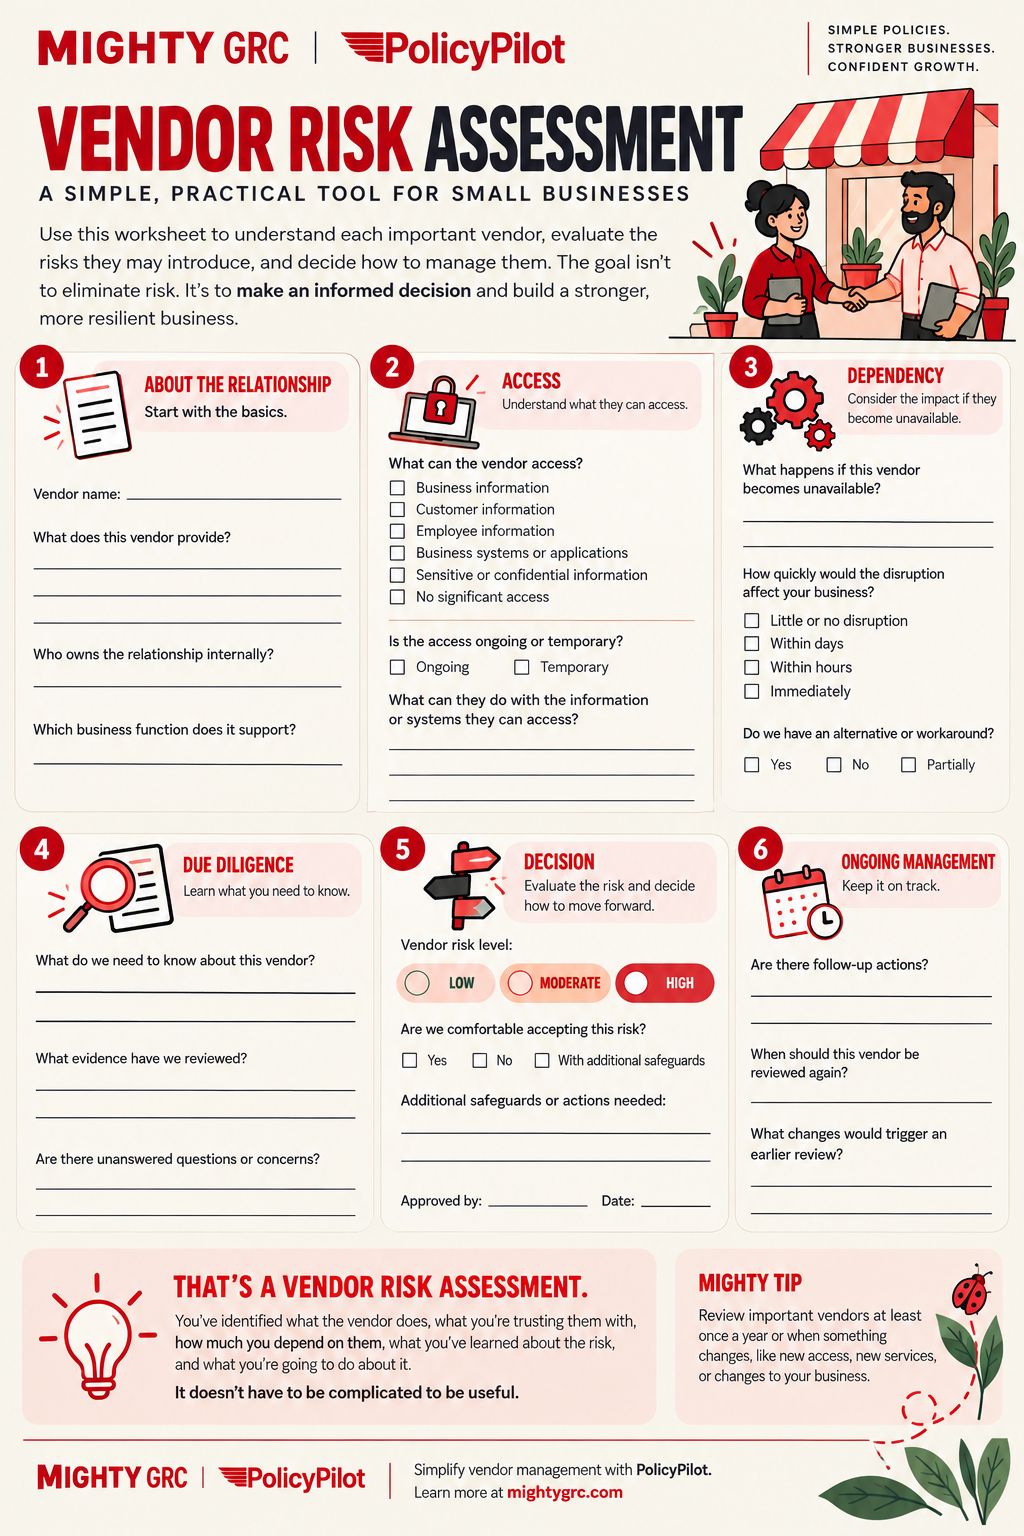
A simple Vendor Risk Assessment template for small businesses
You don't need a complicated scoring model to get started.
For each important vendor, answer:
The relationship
What does this vendor provide?
Who owns the relationship internally?
Which business function does it support?
Access
What information can the vendor access?
What systems can it access?
Is the information sensitive?
Is the access ongoing or temporary?
Dependency
What happens if the vendor becomes unavailable?
How quickly would the disruption affect the business?
Do we have an alternative or workaround?
Due diligence
What do we need to know about this vendor?
What evidence have we reviewed?
Are there unanswered questions or concerns?
Decision
Is the vendor Low, Moderate, or High risk?
Are we comfortable accepting that risk?
Are additional safeguards needed?
Who approved the decision?
Ongoing management
Are there follow-up actions?
When should the vendor be reviewed again?
What changes would trigger an earlier review?
That's a vendor risk assessment.
It can become more sophisticated as your business grows, but starting simple is far better than waiting until you can build the perfect process.
Save and share this infographic with your team!
For businesses that want a more formal starting point, CISA's SMB vendor template and NIST's newer due-diligence guidance provide useful next steps.
CISA's resource is specifically tailored to SMB vendor assessment, while NIST SP 1326 goes deeper into cybersecurity supply-chain due diligence for ICT suppliers.
Your vendors are part of your small business ecosystem
Small businesses accomplish incredible things precisely because they don't do everything themselves.
You use technology. Hire experts. Work with partners. Rely on suppliers. Build an ecosystem around your business that lets a relatively small team accomplish much more.
Vendor risk management helps you build that ecosystem intentionally.
You don't need to investigate every vendor like an enterprise procurement department. You need a practical process for recognizing the relationships that matter most, asking better questions, documenting your decisions, and keeping an eye on those relationships as your business evolves.
Know who you depend on. Understand the risk. Make the decision. Keep moving.
Not sure where to start?
The Mighty Guide to SMB Policies
Get your free MIGHTY Guide to writing your first Vendor Risk Assessment, and take the first steps toward building a practical policy program that includes InfoSec, Acceptable Use, AI, Business Continuity, and more.
Start with a Vendor Risk Assessment. Build a stronger business.
PolicyPilot by MIGHTY GRC helps small businesses turn complex policy requirements into clear, tailored policies built around how their business actually operates.
Turn vendor risk from an occasional questionnaire into a process your business can actually follow.
Answer a few straightforward questions, and in minutes you can:
Customize your Vendor Risk Assessment for your real world business.
Manage policy reviews and approvals in one place.
Use automated reminders to keep your Vendor Risk Assessment current.
Because the goal isn't more paperwork. It's better decisions about the businesses you trust with yours.
Your policies should be simple. They should be actionable.
And they should actually get used.
Explore PolicyPilot today and start building your Vendor Risk Assessment in minutes.
Thank you from the MIGHTY team. We are dedicated to offering learning resources for small and midsized businesses that are supportive, actionable, and will actually get used.
This article is provided for educational and informational purposes only. It is intended to help small businesses better understand governance, risk, compliance, and policy management, but it is not legal, financial, cybersecurity, insurance, or other professional advice.
Use this content as a starting point for building a stronger, more resilient business—not as a substitute for professional advice tailored to your specific needs.
 The terminology can make the process sound complicated but you're just trying to understand what you're trusting another organization with.
 Before you start thinking about risk levels, questionnaires, or due diligence, start with something simpler:
 Next, ask:
 Now look at what you're trusting the vendor with.
 Vendor risk isn't only about data breaches.
 Not sure where to start? Our
 You now know two important things:
 This is where vendor risk management can become unnecessarily complicated.
 Once you know how closely you need to evaluate a vendor, you can decide what you actually need to know.
 A questionnaire tells you what a vendor says, or is willing to admit, about its practices, processes, and people.
 A vendor risk assessment isn't useful or actionable if it ends up simply being a completed questionnaire sitting in a folder.
 Approving a vendor isn't a one-time process for your small business.